An audit that tells you something you didn't already know
Most internal audit programmes stop being useful after a few cycles. Not because anyone is doing them badly, but because the same person keeps looking at the same processes and stops seeing them.
I conduct internal audits and supplier audits as an independent auditor. The value isn't extra capacity. It's that I have no history with your system, no relationships to protect, and no reason to skip the thing everyone has agreed not to talk about.
I also audit suppliers and contractors for companies who don't have the internal resource to do it themselves.

28 years in life sciences across three continents
Experience with USFDA, TGA and MHRA audits
What a good internal audit programme gives you
Findings you can act on.
Ranked by criticality, with the evidence attached, so you can decide where to start.
Risks found before a regulator finds them.
That's the whole commercial case for internal audit and it's worth stating plainly.
The system behind the finding, named.
An isolated problem and a structural one look identical on an audit report. They need entirely different responses.
A schedule that follows risk rather than the calendar.
Coverage is not the same thing as insight.
A report someone actually reads.
Most quality managers have a shelf of audit reports nobody has opened since the closing meeting.
What a supplier audit gives you
Supplier audits are part of your regulatory compliance. They confirm that the partners you work with meet GxP requirements, through an assessment of their quality systems and their GxP activities.
They also give you something comparable. If every supplier is assessed on the same basis, a decision between two of them can be defended.
Why the same findings keep coming back
The audit checked the documents, not the practice. The procedure exists, so the box gets ticked. Whether anyone follows it is a different question and it takes longer to answer.
Findings get closed rather than solved. Closure is measured and reported. Resolution isn't, so closure is what you get.
The same auditor has the same blind spots. Familiarity is the enemy of an audit. After the third cycle you're looking at what you looked at last time.
The schedule is driven by the calendar. Twelve audits a year because there are twelve months, rather than because that's where the risk is.
You'll recognise some of these
The same observations turn up every cycle
Audit reports that sit unread
Audits scheduled to hit a number
Suppliers assessed on a questionnaire and nothing else
Findings with no owner attached
No line from audit results to management review
The audits I conduct
Internal audits. An independent look at your own systems as they're operated rather than as they're written. The value is the outside view your own team structurally can't give you, however good they are.
Supplier and contractor audits. Assessment of the organisations you depend on, against the GxP requirements that apply to your product, including travel to their sites. If you're a smaller company without the internal resource to manage this, it's often the first thing worth bringing in from outside, because the risk sits in someone else's building and you have the least visibility of it.
If a regulator or a customer is auditing you and you want support through it, that's different work and it's on the compliance assessments page.
What an audit covers
Practice, not just paperwork. Walkthroughs and observation as well as records. You find different things when you watch the work happen.
Whether a finding is isolated or structural. This is the difference between an audit and a checklist.
Risk-based scope. Depth where the consequence is highest, rather than even coverage of everything.
Whether findings reach the people who can act on them. Audit output that never gets to management review is a cost with no return.
What you receive
An audit report with findings and evidence.
What was observed, against which requirement, with what supports it.
A criticality rating on every finding.
So you can sequence your response by risk rather than by the order things appear in the report.
A follow-up and closure process.
Agreed checkpoints, so findings get resolved rather than just closed.
A debrief with the people involved.
Findings explained to the people who'll act on them.
What you won't get is recommendations
An auditor's job is to assess whether the systems you have implemented comply with regulatory requirements, and whether they're effective. That means objectively assessing whether your procedures and controls meet those requirements, and whether they actually protect patient safety and product quality. For a supplier audit, it means assessing whether a contractor and their systems are capable of meeting the regulations that apply to your product.
Recommendations don't form part of that. An auditor who designs the fix ends up assessing their own work.
If what you want is recommendations and a prioritised plan, that's a gap assessment, and it's a different piece of work.
Where this connects
If you want the fixes as well as the findings.
A gap assessment gives you recommendations and a prioritised plan.
If the findings point at the system itself.
If the gap is capability rather than process.
How you'd know it worked
Whether repeat observations drop.
How long findings take to close.
Whether you can see supplier risk across your whole base rather than one at a time.
Whether audit findings are reaching management review at all.
Audits I've conducted
Overview of audits performed to September 2026.
| Audit type | Scope |
|---|---|
| Contract test laboratory, Australia | Microbiology testing laboratory, audited against PIC/S Guide to GMP Part 2, laboratory controls |
| CDMO — Shanghai, China | API manufacturing CDMO audited against PIC/S GMP Part II and associated annexes, on behalf of a drug development start-up |
| Sterile fill-finish CDMO — Australia | Sterile fill-finish facility audited against PIC/S GMP Part I |
| IMP storage facility — Australia | Investigational medicinal product storage facility audited against PIC/S GMP Parts I and II, specifically Annex 13 |
| Gamma irradiation facility — Belgium | Audit of a gamma irradiation facility used for sterilising a drug product |
What an audit can surface
During a contractor audit of a manufacturing site, I found non-compliances across several GMP documents. The document system was a mix of electronic and paper records with no clarity on how either was controlled or tracked, and traceability gaps ran across three separate functions.
That pointed at a failure of the document management system at the site rather than a set of isolated errors. The finding let the sponsor describe their documentation and traceability requirements precisely, and build them into the contract and the quality agreement.
A future regulatory finding against the sponsor's product, manufactured at that site, was averted.
How an audit runs
1. A conversation.
Thirty minutes to understand the scope, whether it's internal or supplier, and what's prompted it.
How an audit runs
2. Scope and schedule.
Risk-based scoping and an agreed plan you can circulate internally or send to the supplier.
How an audit runs
3. The audit.
On site or remote. Walkthroughs and observation as well as records. You get feedback as we go rather than a surprise at the closing meeting.
How an audit runs
4. Reporting.
Findings with evidence and criticality ratings, plus a debrief.
How an audit runs
5. Follow up.
Agreed checkpoints to confirm findings were resolved rather than closed.
Who you'd be dealing with
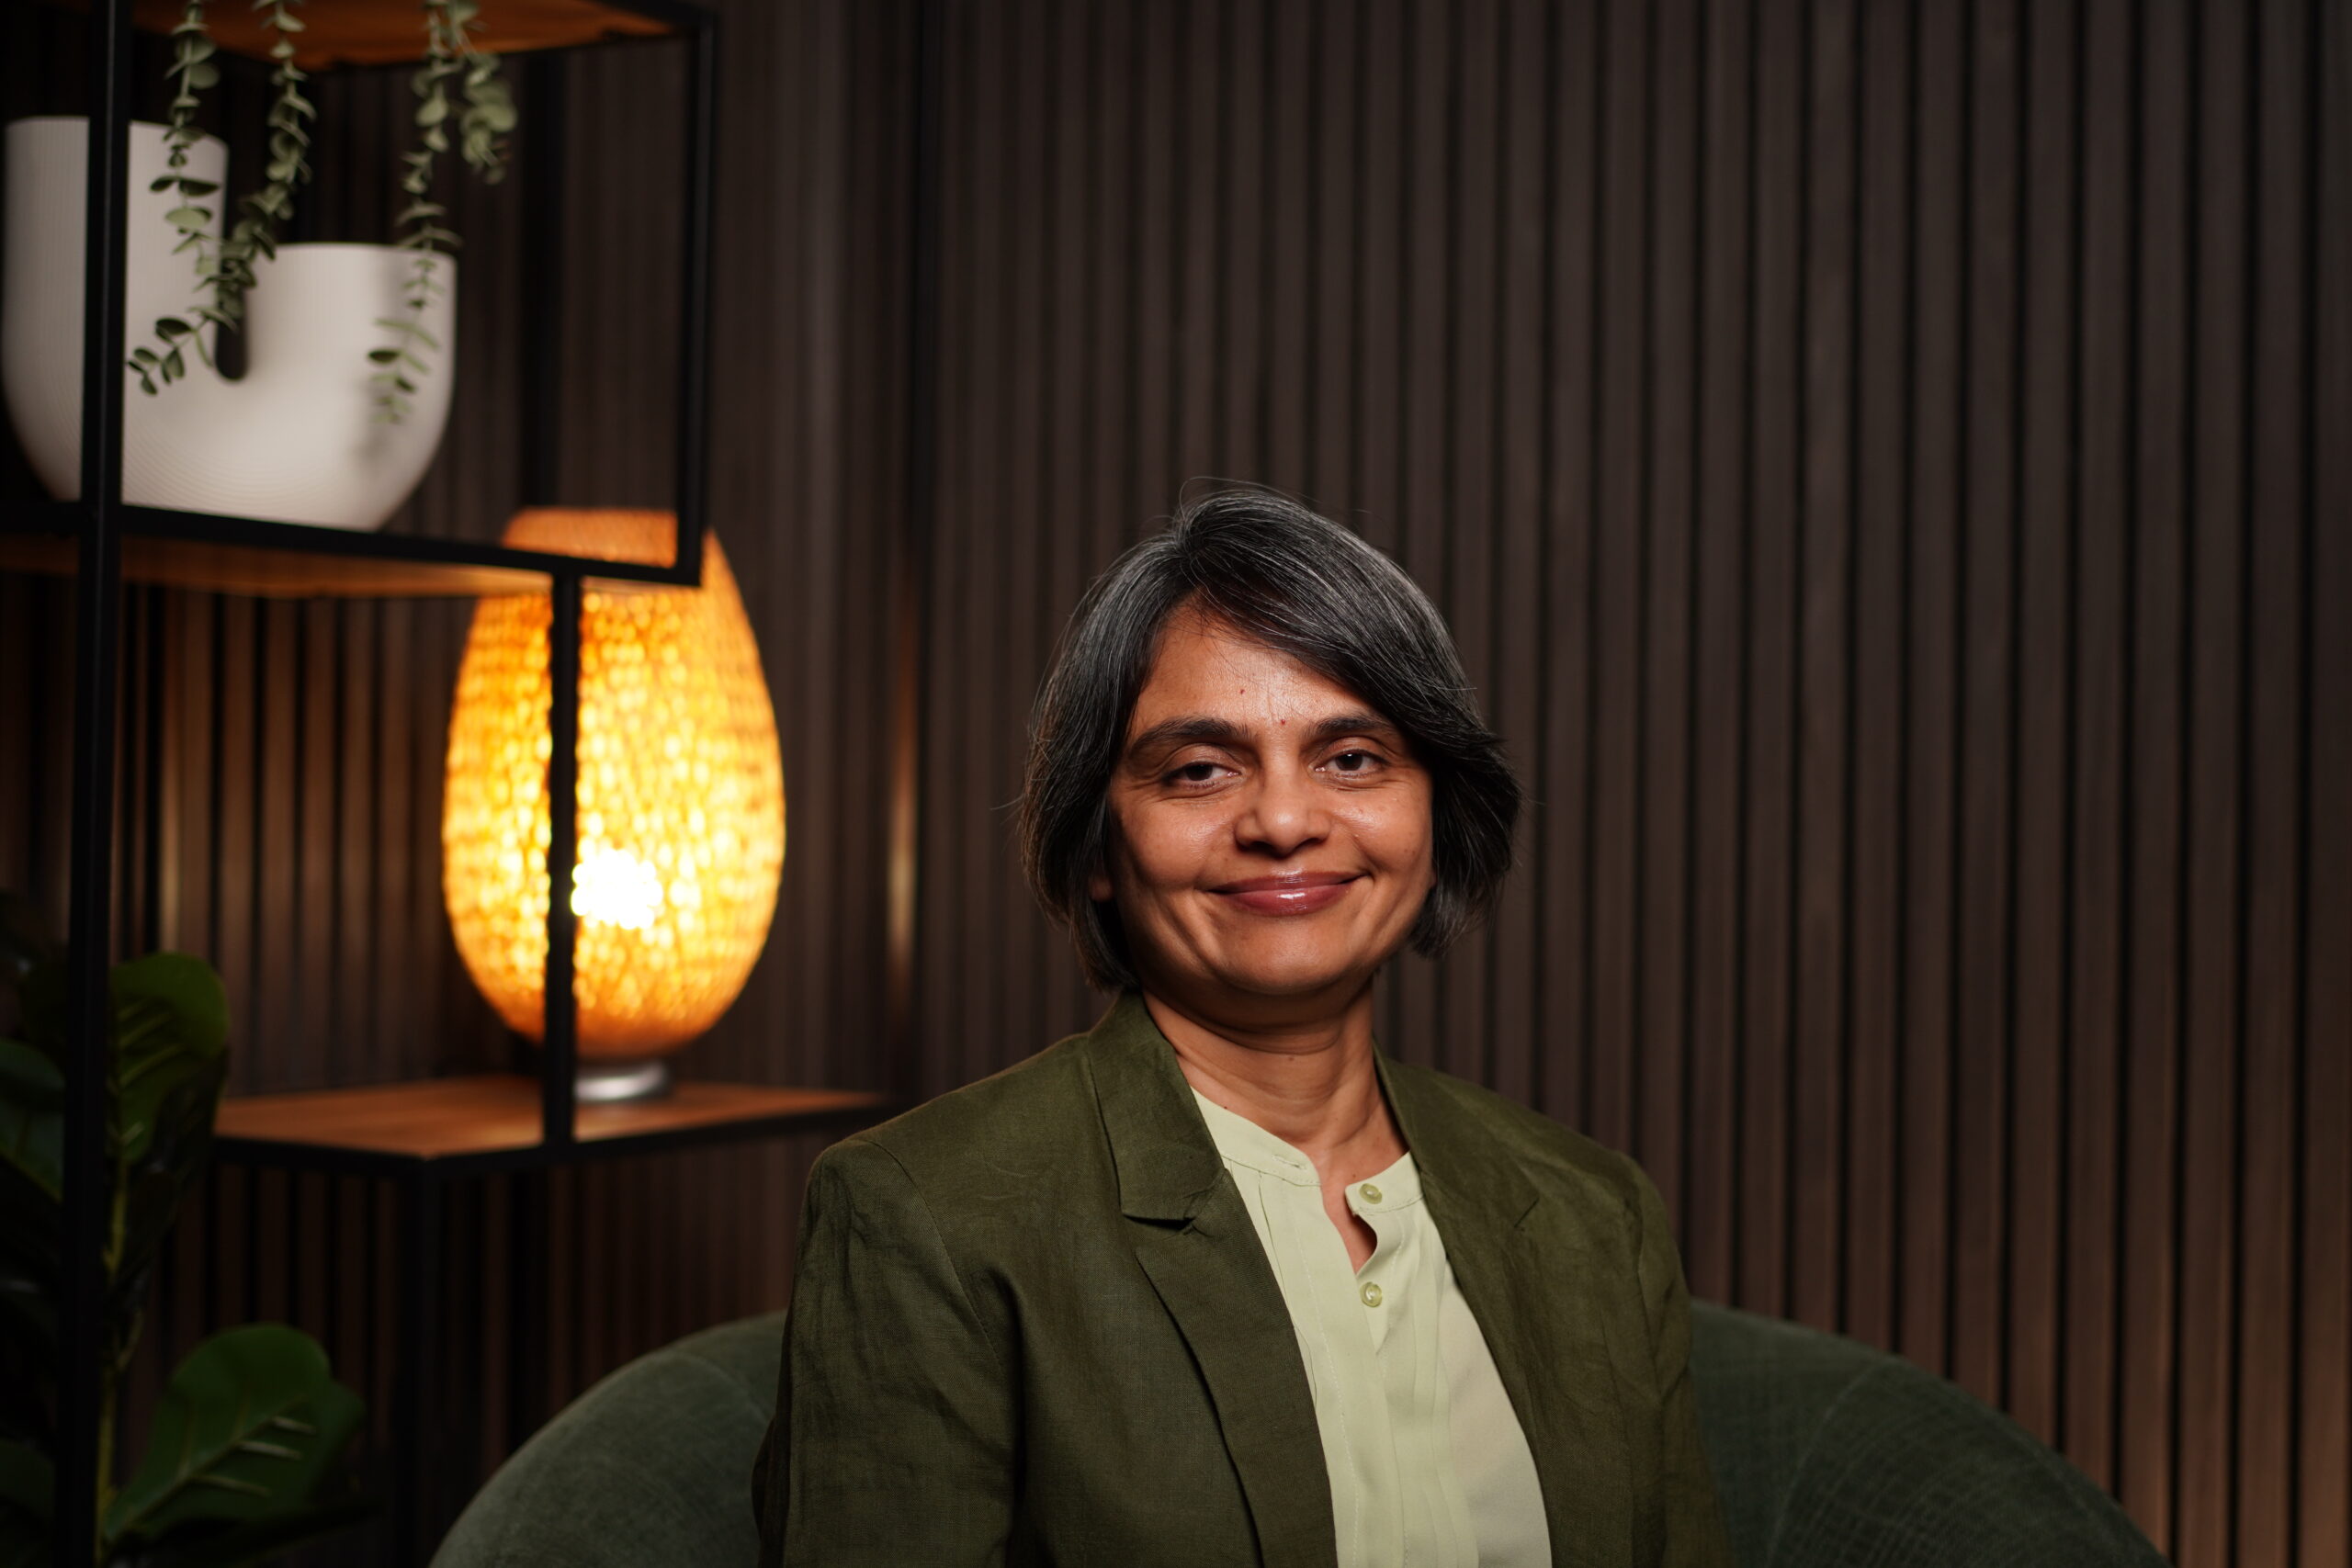
I'm Antiksha Joshi. I've spent 28 years in pharmaceutical and life sciences quality across three continents. I am Chair of Women in Pharma, ISPE Australasia Affiliate.
I also write and speak on quality systems for various knowledge sharing organisations and online publications.
I've audited API manufacture, sterile fill-finish, contract testing laboratories, IMP storage and sterilisation facilities, in Australia, China and Europe. I also facilitate training on effective internal auditing, which means I've had to think carefully about what separates an audit worth doing from one that fills a slot in a schedule.
I don't resell software and I have no commercial relationship with any system vendor, which matters more in this work than in most.
Questions people ask
What's the difference between an internal audit and a supplier audit?
Internal audits look at your own systems. Supplier audits confirm that the partners you depend on meet the GxP requirements that apply to your product. The approach and the outcome are different, even though the method looks similar from outside.
Why don't auditors give recommendations?
Because an auditor's job is to assess compliance and effectiveness objectively. If I design the fix, I end up assessing my own work. If you want recommendations, ask for a gap assessment instead and you'll get them.
How often should we be auditing?
Based on risk rather than on a fixed number. I'd rather help you build a schedule that reflects where your exposure actually sits.
Can you audit our existing suppliers?
Yes, including travelling to their sites, in Australia or overseas.
We don't have anyone to manage supplier audits. Can you handle it?
Yes. That's common with smaller companies and it's often the most sensible thing to bring in from outside.
What happens after the audit?
You get the report and a debrief, and we agree follow-up checkpoints. What you do with the findings is yours, and I'm happy to help separately if you want that.
Can you work alongside our QA team?
Yes. Your QA people usually know exactly where the problems are. An independent audit gives them something they can act on.